31 de out. de 2026 · Victor Slompo
Your coding agent is only as safe as its extensions
A backdoored Claude Code extension hit the Cursor Marketplace.
WHAT HAPPENED
A tampered Claude Code extension shipped with an SSH backdoor
Phorion detected a backdoor in the Claude Code for VS Code extension on the Cursor Marketplace. Cursor removed versions 2.1.312 and 2.1.313. The payload runs as soon as the file loads, with no user interaction needed.
THE NUMBER
5,000
developer systems impacted, according to Cursor
Figure as reported by DoublePulsar, citing Cursor.
THE REAL PROBLEM IN COMPANIES
What I see in companies adopting coding agents
- 01Extensions install and auto-update, and nobody owns the approved list
- 02Agents and IDEs run with the full access of the developer's machine
- 03Nothing sits between a new tool and production code or credentials
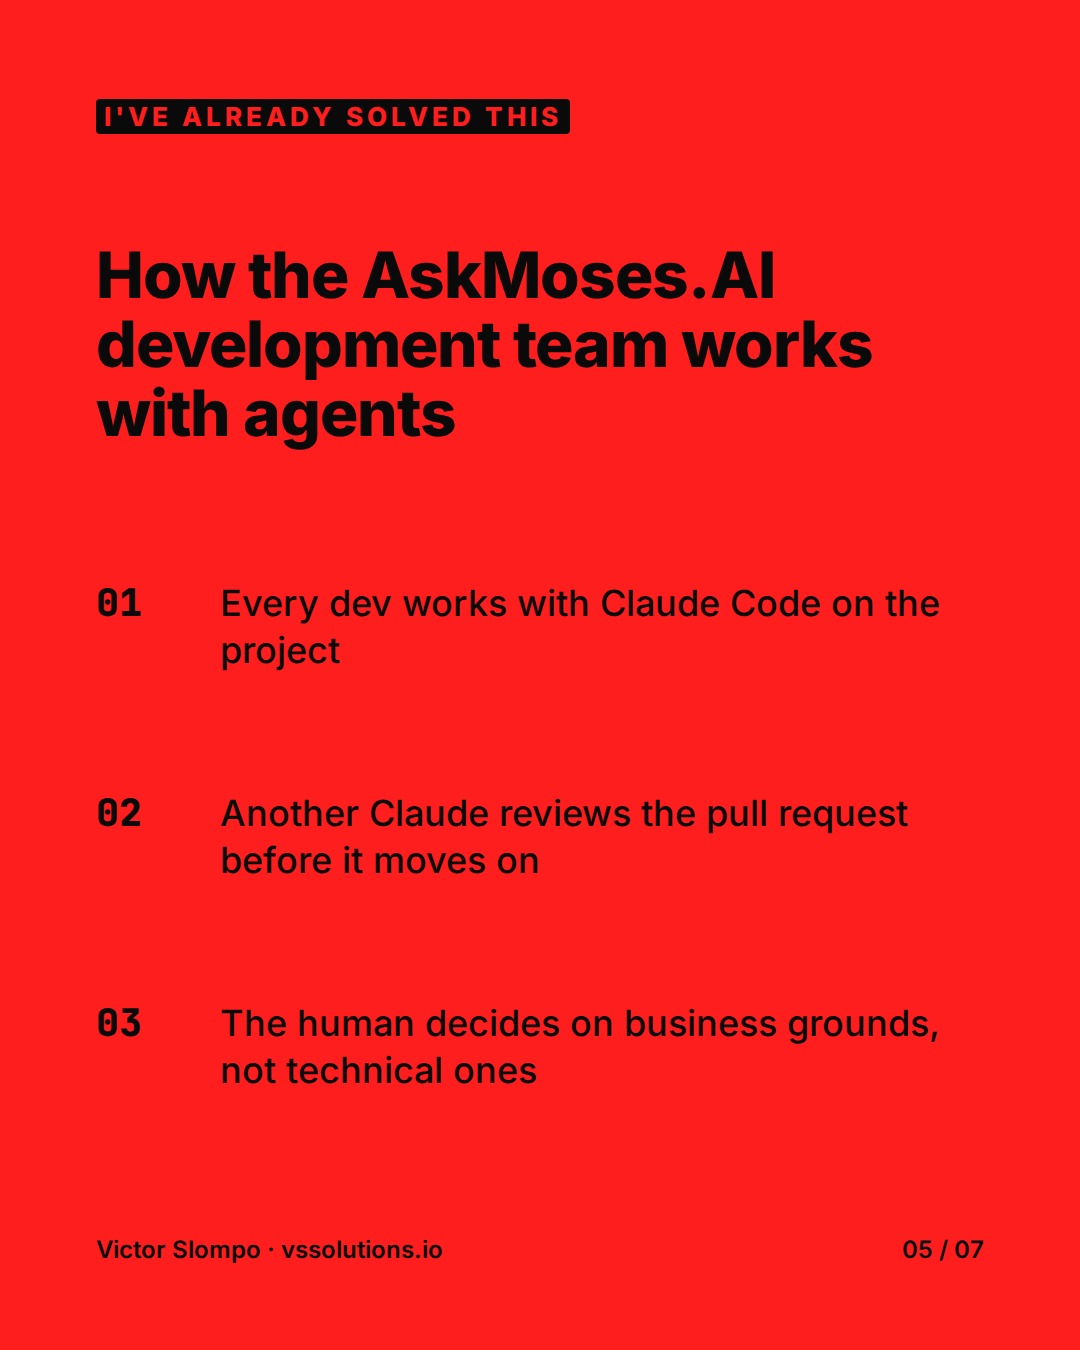
I'VE ALREADY SOLVED THIS
How the AskMoses.AI development team works with agents
- 01Every dev works with Claude Code on the project
- 02Another Claude reviews the pull request before it moves on
- 03The human decides on business grounds, not technical ones
- 04Deploys on Vercel with 1-click rollback and daily backups
MY TAKE
Launching is not the same as being used.
This also applies to safety. An allowlist, least-privilege access and a review gate only matter if they are enforced every day. A policy nobody follows is not a control. Measure what your agents can reach, instead of assuming.
Fontes
Quer isso funcionando na sua empresa?
Eu tiro IA do papel e coloco em produção, com resultado medido. No Instagram, comenta CLAUDE no post e eu te mando o passo a passo no direct.